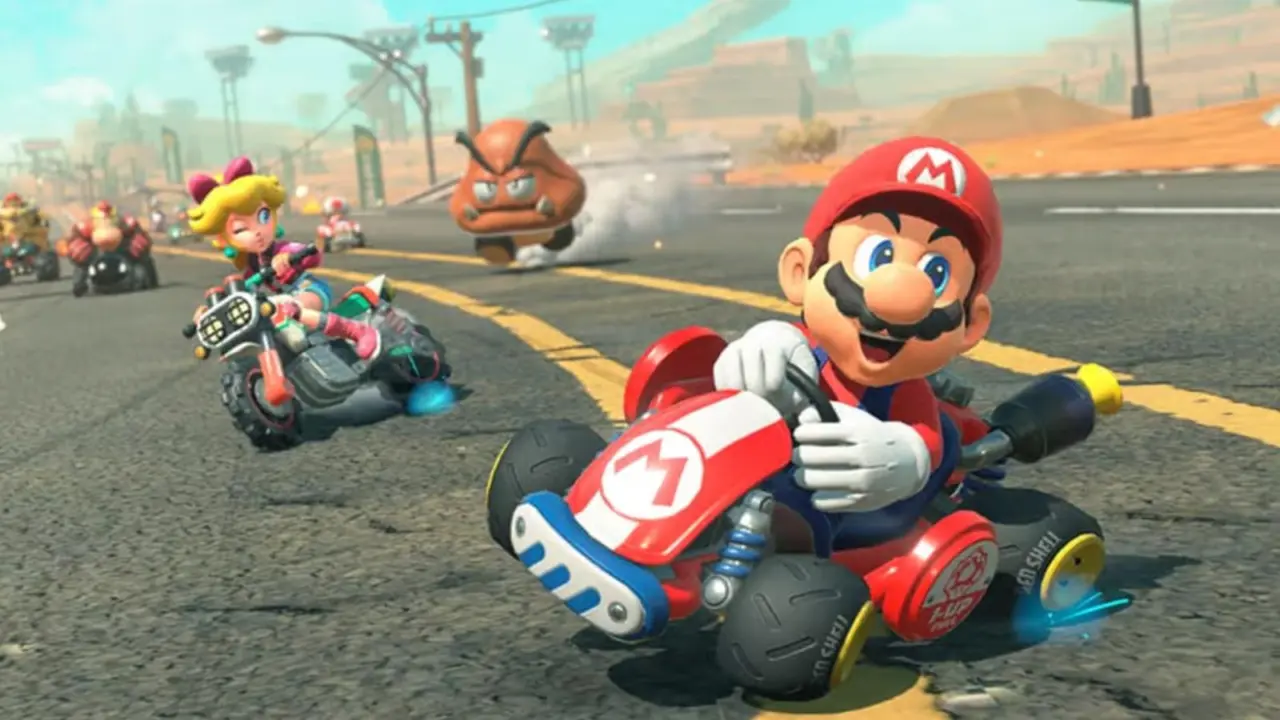
A security expert used AI to expose a vulnerability on Nintendo Switch 2, and Nintendo pulled the software from digital outlets. This affects owners because it demonstrates the immediacy of Nintendo’s response to publicly exposed security issues on their first party development kits. The removal of SmileBASIC will impact anyone using it to develop or hack games.
Nintendo pulls development software after AI exploit
AI was used by pepsipu to exploit a vulnerability on SmileBASIC. The memory overwriting capabilities granted by that exposure led to the alteration of the game Mario Kart World during the testing process. The exposure serves to show how AI-enhanced security testing can reveal weaknesses on the custom development kits of Nintendo.
It's important to note that the obtained jailbreak is tethered, so it's not permanent after a reboot. The fact that it requires a reboot to enable the exploit once again makes this hack not a permanent kernel-level infiltration. You’ll have to re-enable the exploit every time you restart your console in order to get the altered state again.
Nintendo has not commented on the hack or the removal of SmileBASIC officially. The lack of any kind of official comment on the situation leaves us wondering how the development software will be handled in the future. It puts a spotlight on the dangers of using beta or development software in public facing situations.
We touched on many of the same balance/stability issues with the last update we saw on Nintendo Switch 2. This situation only serves to further emphasize the importance of keeping security vigilant on the platform. With the removal of SmileBASIC the very tangible effect of this particular vulnerability exposure.
Source: IXBT
Discussion
0 comments