GAMES Bombora updates Heroes of Might and Magic book cover after fan backlash GAMES Resident Evil 7 saved Capcom’s franchise after a chaotic development marked by internal disputes NINTENDO SWITCH Culdcept BEGINS PC release confirmed for October 28, 2026 GAMES GTA 6 narrows roads and limits weapons to force tactical play AMD Topfeel DeskOne A1 packs 24-core Intel Core Ultra 9 and 256 GB RAM in a 21-liter chassis GAMES iQOO Pad Pro brings 165Hz OLED and active cooling to an 8.8-inch gaming tablet NVIDIA Axera AX8860P targets Nvidia DGX Spark with 256 TOPS AI accelerator for under $2,000 AMD Microsoft weighs spec cuts for cheaper Surface as Apple MacBook Neo pricing pressures margins DLSS NCSoft Cinder City Trailer Reveals Tactical MMO Shooter Set in Post-Apocalyptic Seoul CONSOLES 98.6% of Gears of War: E-Day sales in Spain were physical copies GAMES Xbox Manager Deletes X Account After Backlash Over AI Game Development Claims GAMES CD Projekt delays The Witcher 4 details to ensure Ciri is not a copy of Geralt GAMES Assetto Corsa EVO update 0.10 adds 1:1 German Eifel map and off-road driving on December 9 GAMES Games Workshop Unveils Seven New Warhammer 40,000 Battleforce Boxes

Creative Sound Blaster Katana V2X Remote Exploit Published, No Patch Coming

NicoGG 1 min read

A remote exploit for the Creative Sound Blaster Katana V2X allows keystroke injection from up to 15 meters. No patch is coming. Learn about the flaws and mitigation.

Creative Sound Blaster Katana V2X Remote Exploit Published, No Patch Coming
PC HARDWARE

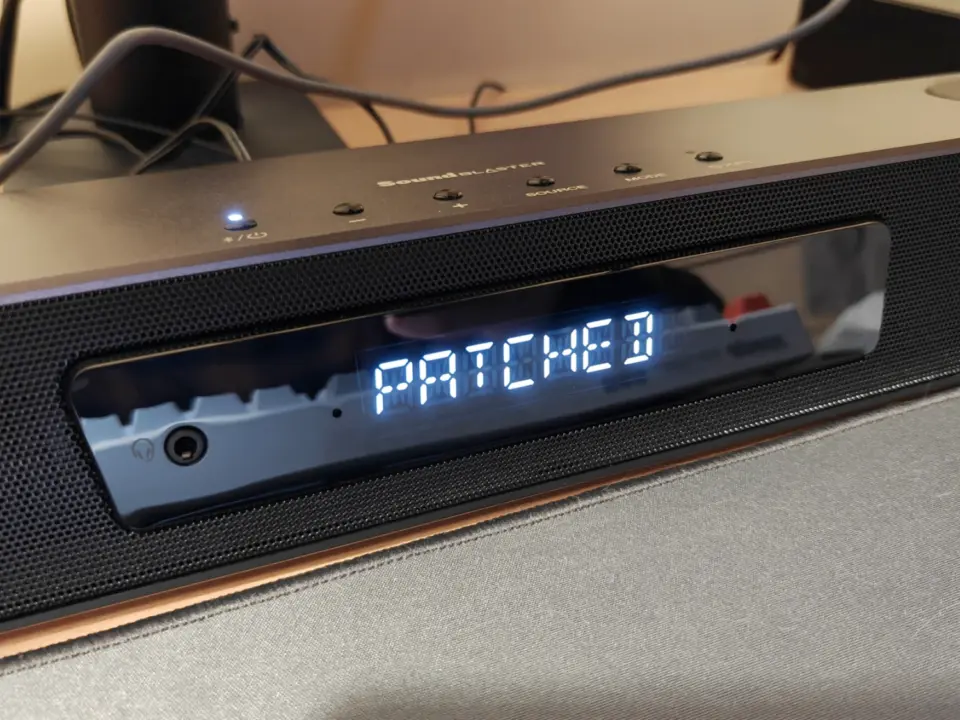
A security researcher has published a remote exploit for the Creative Sound Blaster Katana V2X, a popular PC soundbar. The attack requires no physical access or pairing and can inject keystrokes from up to 15 meters away.

Exploit chains two critical flaws

The exploit chains two flaws in the Katana V2X. First, the Bluetooth Low Energy interface exposes its command protocol without authentication. Second, the speaker accepts firmware updates without cryptographic signing.

An attacker can flash custom firmware over BLE from up to 15 meters without pairing. The custom firmware adds a keyboard HID descriptor, allowing keystroke injection after reboot. The speaker's Bluetooth radio stays active even in sleep mode.

Creative was notified via SingCERT after direct contact attempts failed. Creative responded that this is not a vulnerability. No patch is coming.

A third-party mitigation tool, v2x-patcher, blocks CTP-over-Bluetooth at the firmware level. However, it may break the Creative mobile app.

The latest official firmware remains vulnerable. Users may use the mitigation tool or disconnect the speaker when not in use.

Source: NotebookCheck