Intel has shut down its long-running bug bounty program, a move that removes a reliable channel for security researchers to earn payouts for finding flaws in Intel products. This change matters because it shifts the burden of vulnerability discovery from a paid, structured system to an unpaid disclosure model, potentially reducing the volume of high-quality reports Intel receives. Researchers who previously relied on the program for income must now adjust their workflow or find alternative platforms for compensated security work.
Intel shifts to unpaid disclosure model as AI floods security research with low-quality submissions
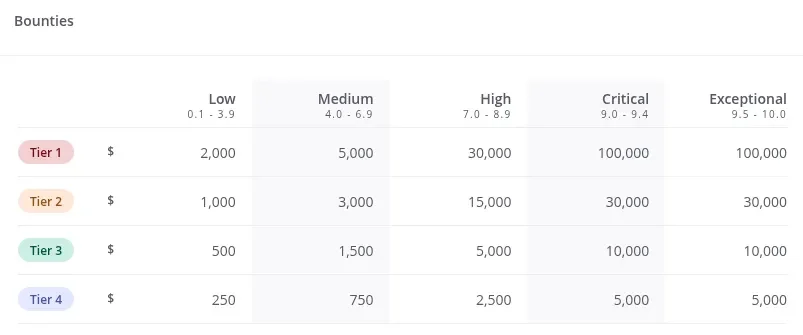
The program, which launched in 2018, covered hardware, firmware, software, and open-source projects associated with Intel. It offered payouts of up to $100,000 for critical security vulnerabilities, incentivizing deep technical analysis of Intel's complex product stack. In 2020, the program was responsible for identifying 105 out of 231 CVEs addressed by the company, demonstrating its significant role in Intel's security posture during that period.
Intel has not provided an official explanation for the suspension, but the timing aligns with broader industry trends where AI-assisted research has flooded other bug bounty programs with low-quality submissions. Programs for the Linux kernel and Curl have seen similar issues, where automated tools generate vast numbers of false positives or minor findings that overwhelm human triage teams. Intel appears to be reacting to this shift by ending the paid incentive structure that may no longer be cost-effective against AI-generated noise.
Security researchers can still submit vulnerabilities through Intel's new Intigriti disclosure program, but this channel does not offer financial compensation for their findings. This transition marks a clear departure from the previous model where substantial rewards were standard for critical flaws. The change reflects a pragmatic adjustment to the current landscape of automated vulnerability detection, prioritizing operational efficiency over paid research incentives.
Source: TweakTown
Discussion
0 comments